Telecommunications
x

Develop Your NIS2 Cybersecurity Roadmap as Soon as You Start Your New Position Using a GRC Platform

As Orange Concessions' first CISO, Yves Bonelli is replacing Excel and PowerPoint with a single repository to manage compliance.
“I’m bringing a tool where the entire framework is already defined—modules that are truly tailored to the SSI—which allow me to manage all aspects of governance and oversight.”
Yves Bonelli
Chief Information Security Officer at Orange Concessions
The challenge
Building a Cybersecurity Framework from the Ground Up in a Company That's Still Taking Shape

Orange Concessions is the Orange Group subsidiary dedicated to Public Initiative Networks. Founded in 2021, Orange Concessions designs, deploys, operates, and markets fiber-optic networks in rural areas.

As a critical entity under NIS2, Orange Concessions is subject to the highest regulatory standards and must be able to demonstrate all the measures it has implemented to comply with them. Yves Bonelli joins the company as its first dedicated CISO, following six years in consulting. He inherits an environment where everything needs to be built from the ground up: a three-year cybersecurity roadmap, several compliance frameworks to manage, and NIS2 compliance to implement—all while working with a GRC platform implemented by the team that preceded him: Tenacy.

The challenge: laying the groundwork for cybersecurity governance—quickly and effectively.

Three convictions upon his arrival:

Centralize management
Consolidate compliance, risks, and action plans into a single repository, rather than juggling unsynchronized Excel and PowerPoint files.
Defining NIS2
Implement the NIS2 (ReCyF) framework operationally and develop a three-year compliance roadmap.
Present to the Executive Committee
Present a clear overview of the gaps and action plans to secure management buy-in.
The objective
A structured cybersecurity strategy that can be implemented as quickly as possible. Move away from static files such as Excel and PowerPoint (which are still sometimes used out of habit) to manage compliance, risks, and action plans from a single GRC platform.
The solution

An all-in-one GRC platform to help you get started in your new role:

A ready-to-use business framework

Modules tailored to the SSI and a predefined framework, which eliminate the need to start from scratch with Excel spreadsheets.

Quick adoption

A powerful platform with streamlined interfaces that a CISO can easily adopt and tailor to their priorities.

Guided support

Methodological CSM oversight to identify priority actions and ensure the success of each stage of implementation.

Table of Contents
Discover how Tenacy structures your cybersecurity
Schedule a demo

‍1/ Establish a single repository rather than piling up files

Over the course of six years as a consultant, Yves Bonelli came to understand the limitations of static files—such as Excel—for managing multi-compliance: forms in different formats, information that needed to be constantly reprocessed, time-consuming updates, and limited visibility over time. Each risk analysis was in one file, each action plan in another, with no link between the two.

With Tenacy, compliance, risks, and action plans are all in one place. The connection between a gap assessment, the associated risk, and remediation becomes dynamic: an updated action item automatically updates the tracking, without the need for re-entry.

“When you conduct a risk assessment and then create a separate file for the action plan, at some point these static elements are no longer in sync. It’s an incredible waste of time. It’s all the behind-the-scenes coordination that makes our lives easier.”
Yves Bonelli, Chief Information Security Officer at Orange Concessions

Covered objective

The Tenacy platform has become Orange Concessions’ single source of truth, used four to five times a week by its CISO. Yves Bonelli now manages governance from a single platform and is able to refocus on his core business, rather than maintaining files.
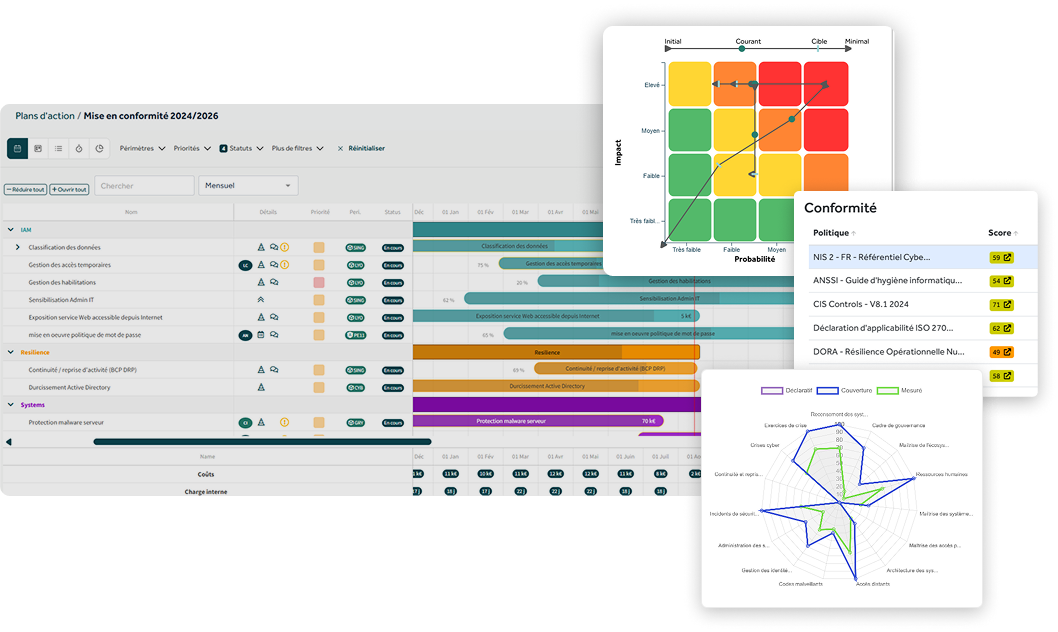
Risks and compliance are linked to action plans in Tenacy

2/ Map NIS2 compliance onto a three-year roadmap

NIS2 sets a high bar that must be anticipated. For a Critical Entity, which has three years to achieve compliance after the regulation takes effect, the path forward is just as important as the current state of affairs. Yves Bonelli reviewed the framework, redefined the measures, established action plans, and developed a multi-year roadmap, prioritizing the most sensitive issues.

The Gantt chart allows him to sequence major projects and present clear projections to management.

“NIS2 is a fairly demanding regulation. Managing it manually would be really complicated.”
Yves Bonelli, CISO at Orange Concessions

Covered objective

Compliance gaps translate into a clear, three-year roadmap—manageable within Tenacy—from the initial audit through to full compliance.


3/ Rely on methodological guidance

Tenacy is a feature-rich platform, and some of its mechanisms take time to master. Rather than proceeding on his own, Yves Bonelli maintained regular communication with the Customer Success Manager assigned to Orange Concessions. This support goes beyond mere technical assistance: it provides a methodological perspective on the solution, the priorities to address, and the potential pitfalls to anticipate.

“It’s a guided approach to getting started with the tool and developing my strategy. Laura (Customer Success Manager at Tenacy) was able to guide me on the essential steps and next actions.”
Yves Bonelli, CISO at Orange Concessions

A Guided Tour

Guidance ensures a smooth transition and prevents missteps. The CISO structures the scope in the correct order, without skipping any key steps.


4/ Demonstrate the cybersecurity roadmap to management

Gaining the executive committee’s buy-in requires making cybersecurity easy to understand. Tenacy ties together compliance, risks, and action plans into a cohesive view, which Yves Bonelli incorporates directly into his presentations and quarterly committee meetings without having to rebuild a PowerPoint presentation from scratch.

“I provide an overview that includes the gaps and the action plans to be implemented. It’s a pretty smooth process; they really like it, and I can present it fairly easily.”
Yves Bonelli, Chief Information Security Officer at Orange Concessions
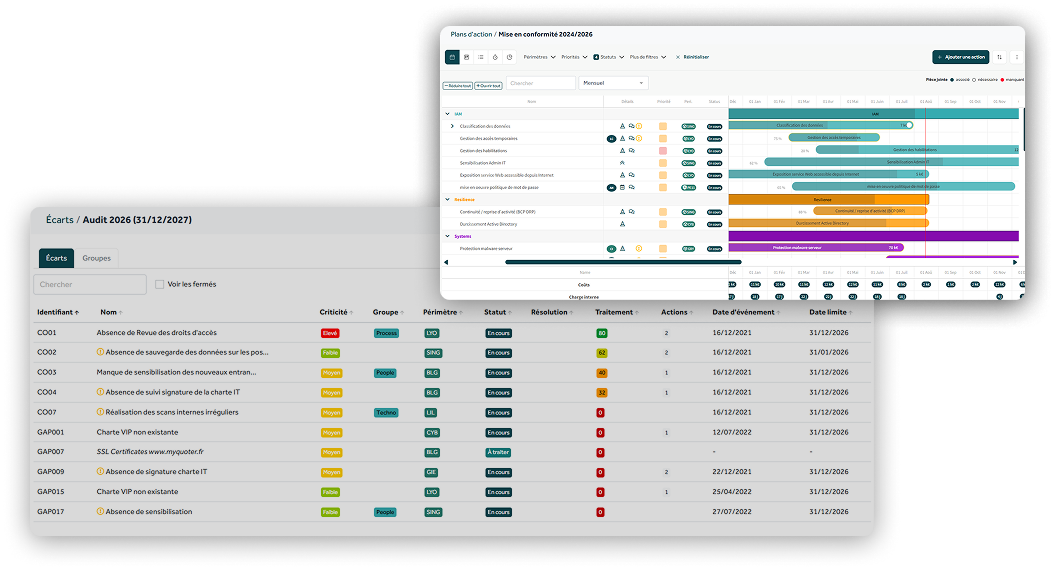
Action plans generated based on variances, centralized in Tenacy

Covered objective

Reporting to the Executive Committee is based on up-to-date data and a clear framework: compliance, risks, actions, and follow-up. Management reviews the trajectory and provides its approval.

Results

The results

A NIS2 Roadmap That Can Be Adapted

Compliance gaps are prioritized and translated into a three-year compliance roadmap.
“We have a tool that meets our needs and allows us to refocus on our core business. Looking back, I would have saved time by entering everything directly into Tenacy from the start, rather than using Excel and then migrating the data later.” Yves Bonelli, CISO at Orange Concessions

A Single Reference Framework

Compliance, risks, and action plans—all brought together and synchronized on a single platform, which has become the go-to tool for day-to-day operations.

Smooth Executive Committee Reporting

A compliance–risk–action framework presented in a straightforward manner to senior management to secure their support.
Conclusion
This case demonstrates that using a GRC platform makes the most sense when you want to establish a framework for your cybersecurity and build a long-term strategy, especially when taking on a new role.
Do these issues resonate with you?
Schedule a demo

Regain Control of Your Cybersecurity

Schedule My Personalized Demo
30 minutes with no obligation