Cybersecurity Regulatory and Standards Monitoring: A Guide for the CISO
Changing regulations, new standards, industry-specific requirements: for a CISO, regulatory monitoring isn’t an option—it’s an ongoing, strategic activity. This practical guide provides a concrete four-step framework to help you structure your monitoring efforts, define your scope, and turnregulatory information into corrective actions.




This guide will help you:

Key points of the fact sheet

Two complementary types of monitoring to master
A monitoring framework to be developed across three dimensions
Content tailored to each internal audience
About Tenacy
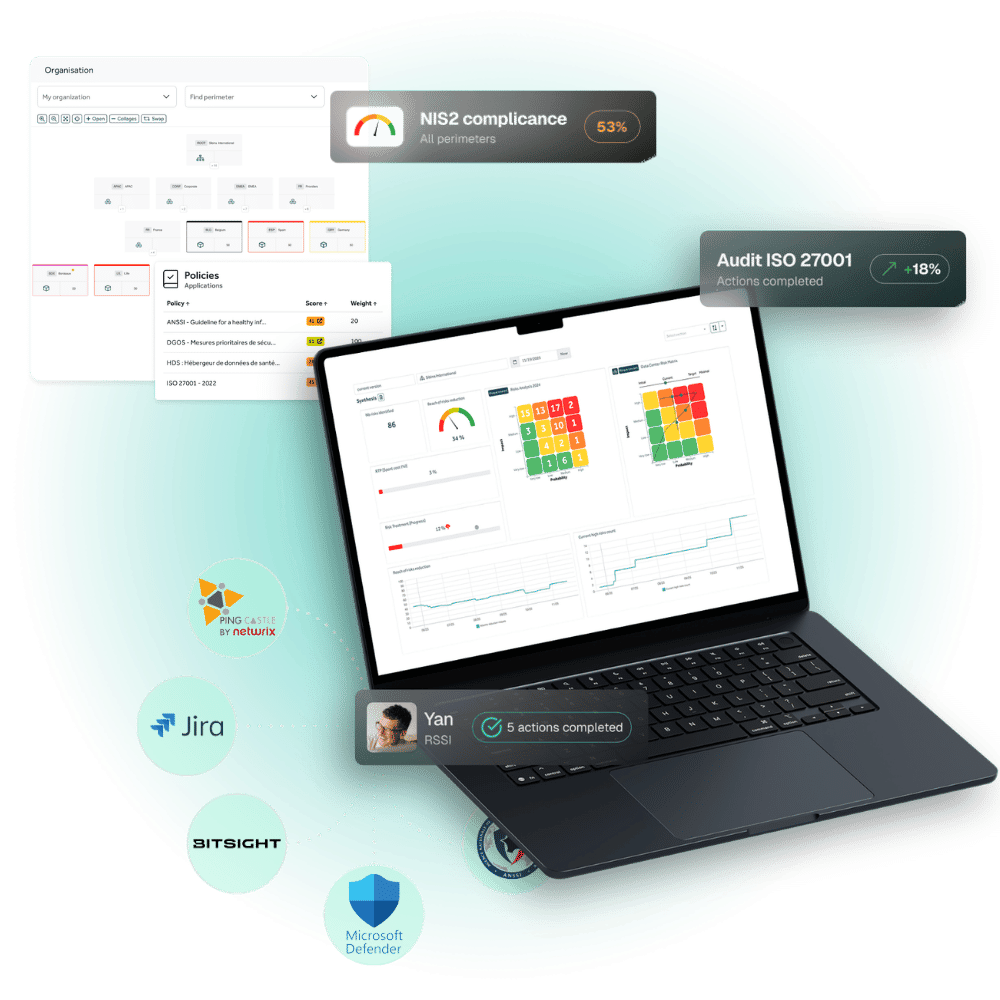
Tenacy is a cyber GRC platform designed for security teams looking to streamline their compliance processes, automate their management, and demonstrate measurable results to senior management.
More than 200 organizations in 32 countries rely on Tenacy to streamline their risk management and multi-compliance efforts (NIS 2, DORA, ISO 27001, etc.).
Find out how Tenacy can transform your organization’s cybersecurity management with a personalized demo: book your demo today.